Strategic cybersecurity
A message for every CEO who does not always listen to their IT manager
Joost Daem, founder of Secamo, on why your organisation’s resilience depends on you, and the six questions to discuss with your IT manager this month.

Your organisation’s resilience rests less on software, audit reports or IT managers than you might think. It rests on luck. Without the right backing from the top, even the best IT manager will not get it done. And that luck factor? That is you, dear CEO.
I am Joost Daem, founder of Secamo. I have worked in cybersecurity for 25 years, the last 15 of them focused on critical infrastructure across sectors. I want to share what I see every day in the companies that struggle with digital security.
“Cybersecurity is tedious, difficult and never solved in one go. But you do not look away, and you back your IT manager on the hard questions.”
Digitalisation
Before digitalisation, you could buy safety: a higher fence, cameras, an automatic gate. Done. Today you have to stay alert every day.
Cybercrime hides in the shortest line of code, in a single moment of inattention. That reality feeds an avalanche of commercial messages flooding IT managers: software and tools that promise the impossible, peace of mind.
Meanwhile your IT manager is caught between a rock and a hard place. With checklists and audits they show that the organisation complies with NIS2. But they lie awake because a large part of the organisation runs on legacy software that can hardly be protected.
Two scenarios
In the companies I visit, I see two scenarios.
Perhaps you are a CEO who sees cybersecurity as a problem for IT. Then do not be surprised if your organisation is not running again within 24 hours after an attack, because three years ago you freed up budget for a recovery plan that was never tested.
Or you are a CEO who knows the reality: cybersecurity is tedious, difficult and never solved in one go. But you do not look away, and you back your IT manager on the hard questions.
Plan a conversation with your IT manager
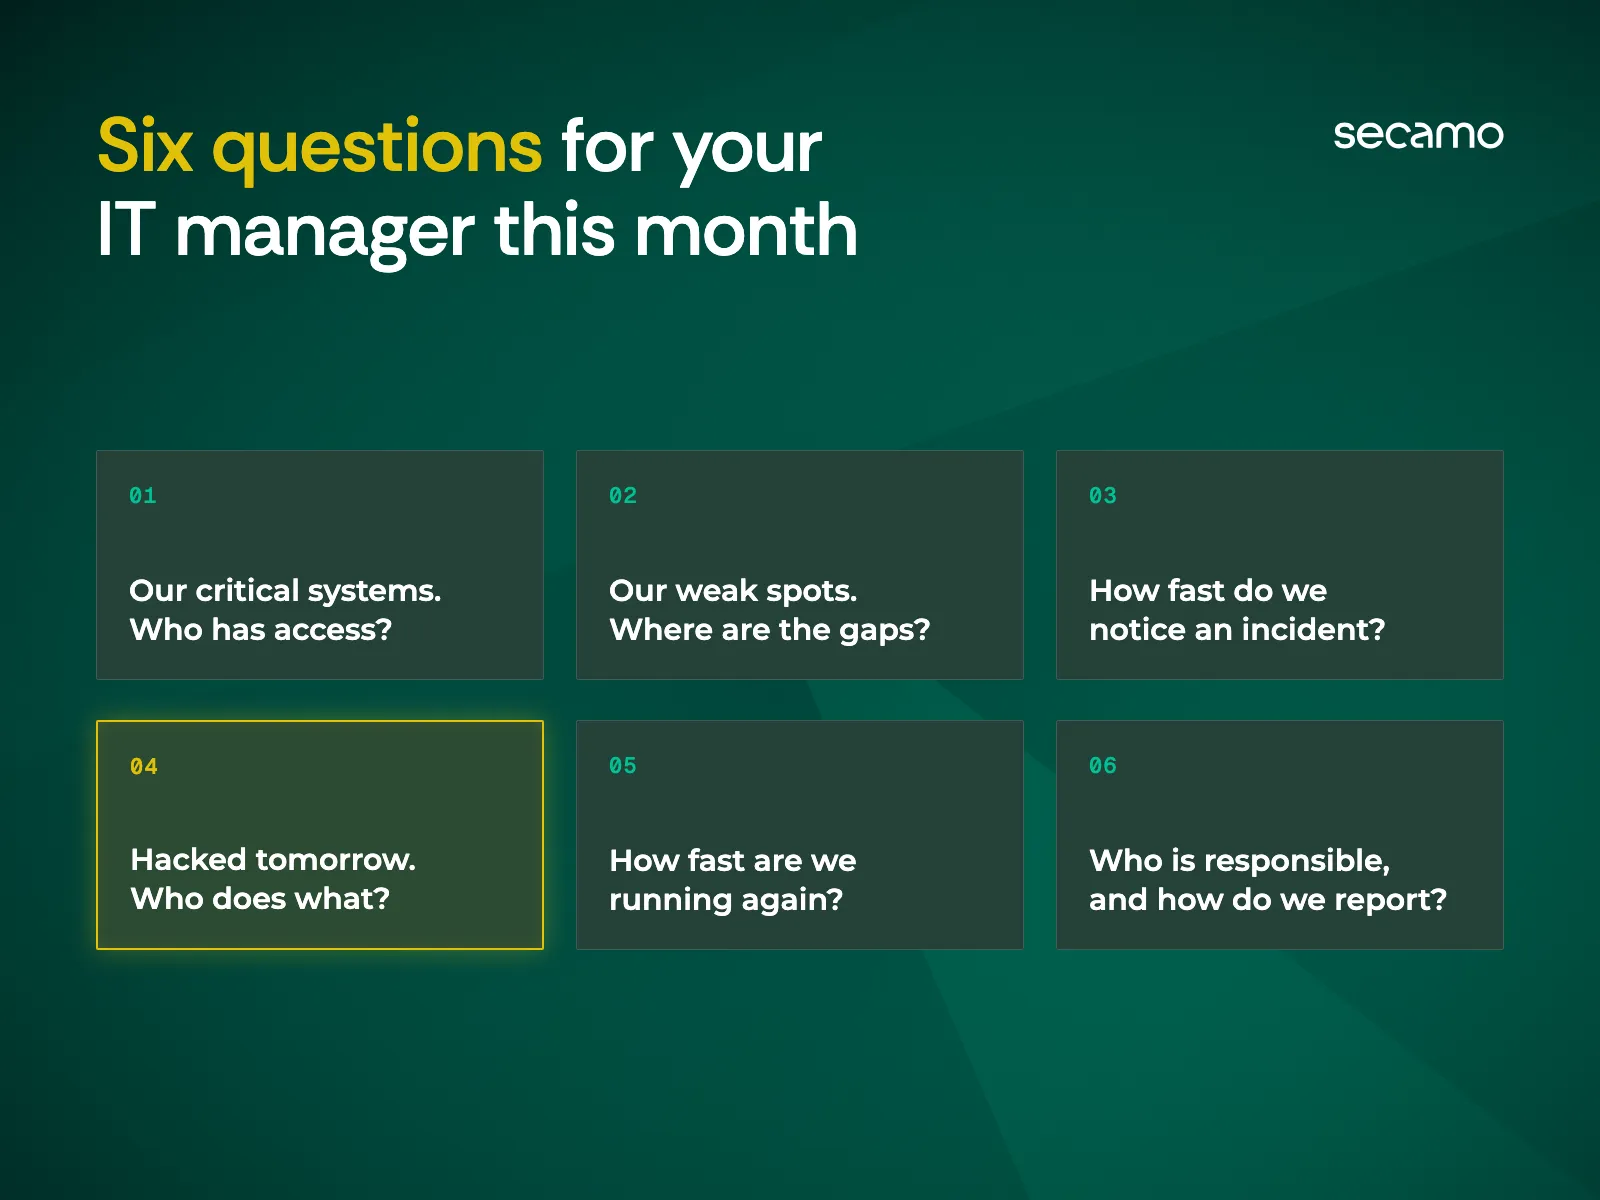
Whatever kind of CEO you are, plan a conversation with your IT manager and go through these six questions:
- What are our most critical systems and data, and who has access to them?
- How do we protect our weak spots, and where are the gaps?
- How quickly do we notice an incident, and how do we know?
- What is our plan if we are hacked tomorrow? Who does what?
- How quickly are we operational again after an attack? What do we need for that?
- Who is ultimately responsible for cybersecurity, and how do we report on it?
The answers will not produce an 80-page report. They will give you an honest conversation about where your organisation stands on digital security.
That is the first step towards real resilience.
Let me know what you think.
Secure for the long run,
Joost