Insights
Lessons from securing what clients build next
Notes from the work of governing, building and running security in organisations where operations cannot stop.
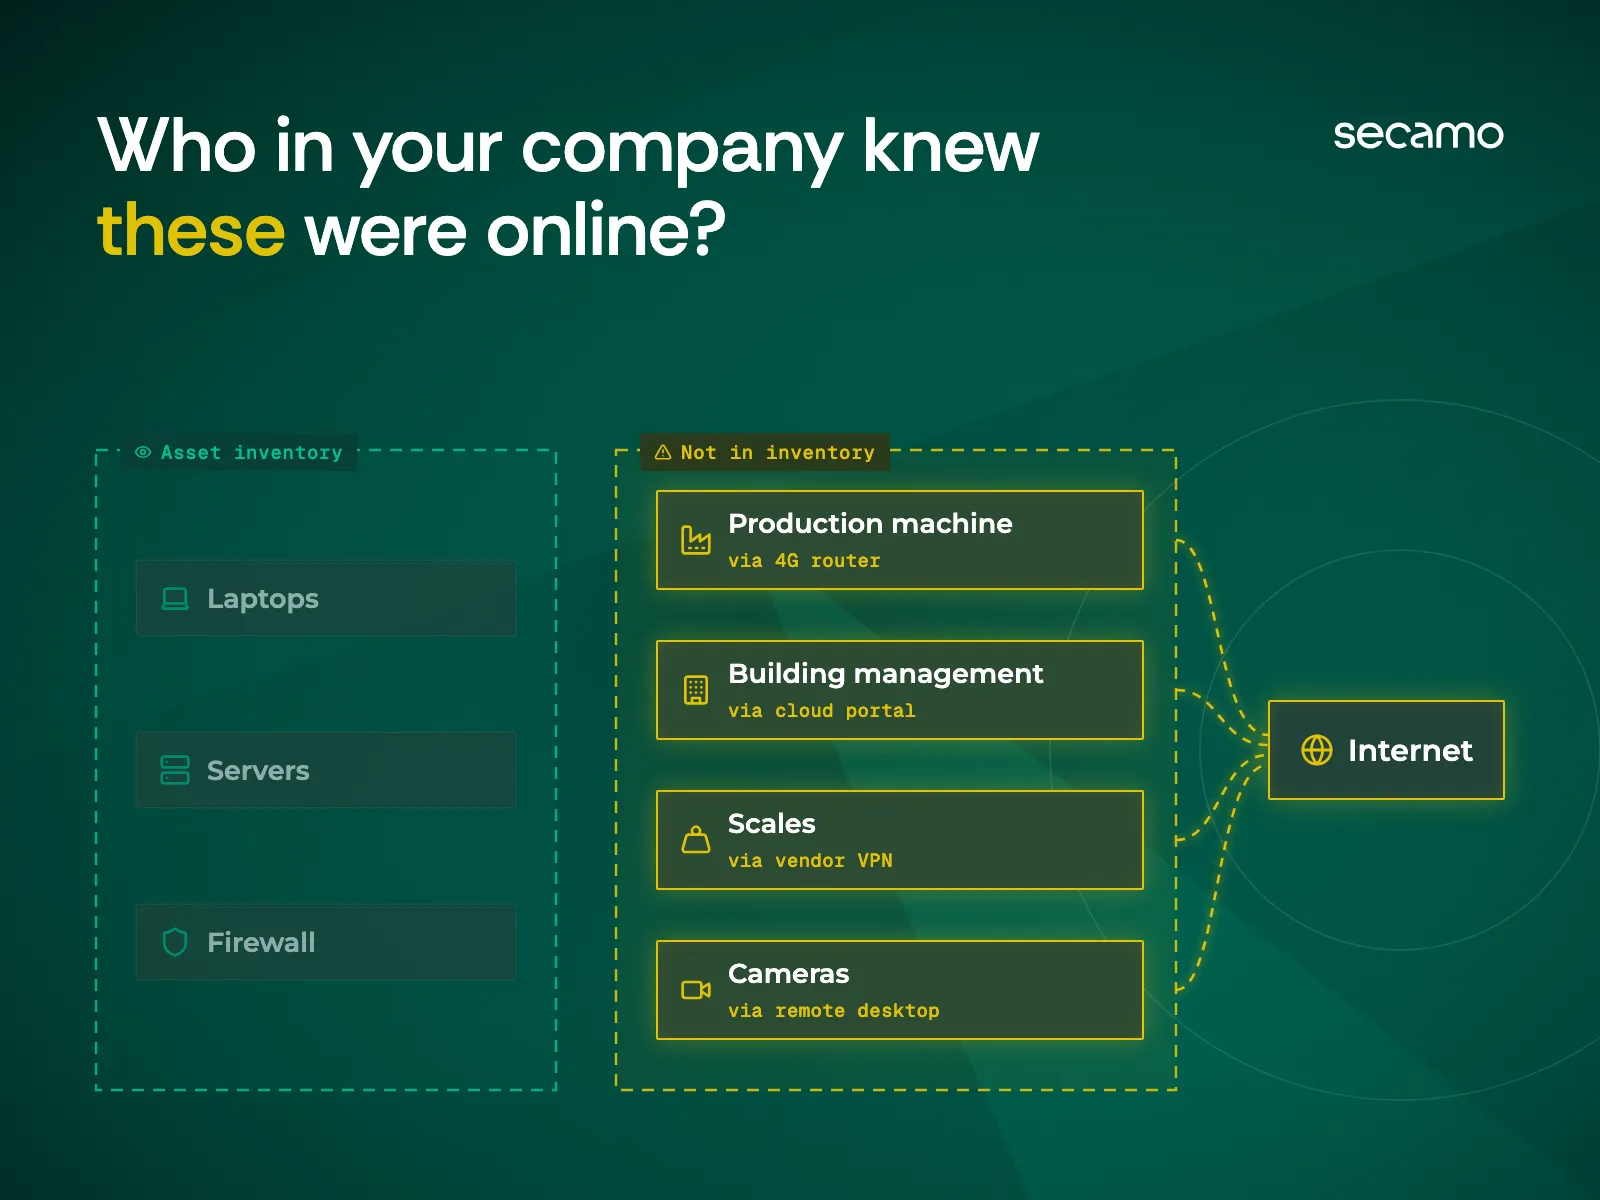
FeaturedSupply-chain security: how to find and control the supplier connections nobody knows aboutThe biggest supply-chain exposure is rarely the software vendor you assessed. It is the supplier whose equipment connects to you and that nobody has on a list. Five practical steps to find and control it. Read the article
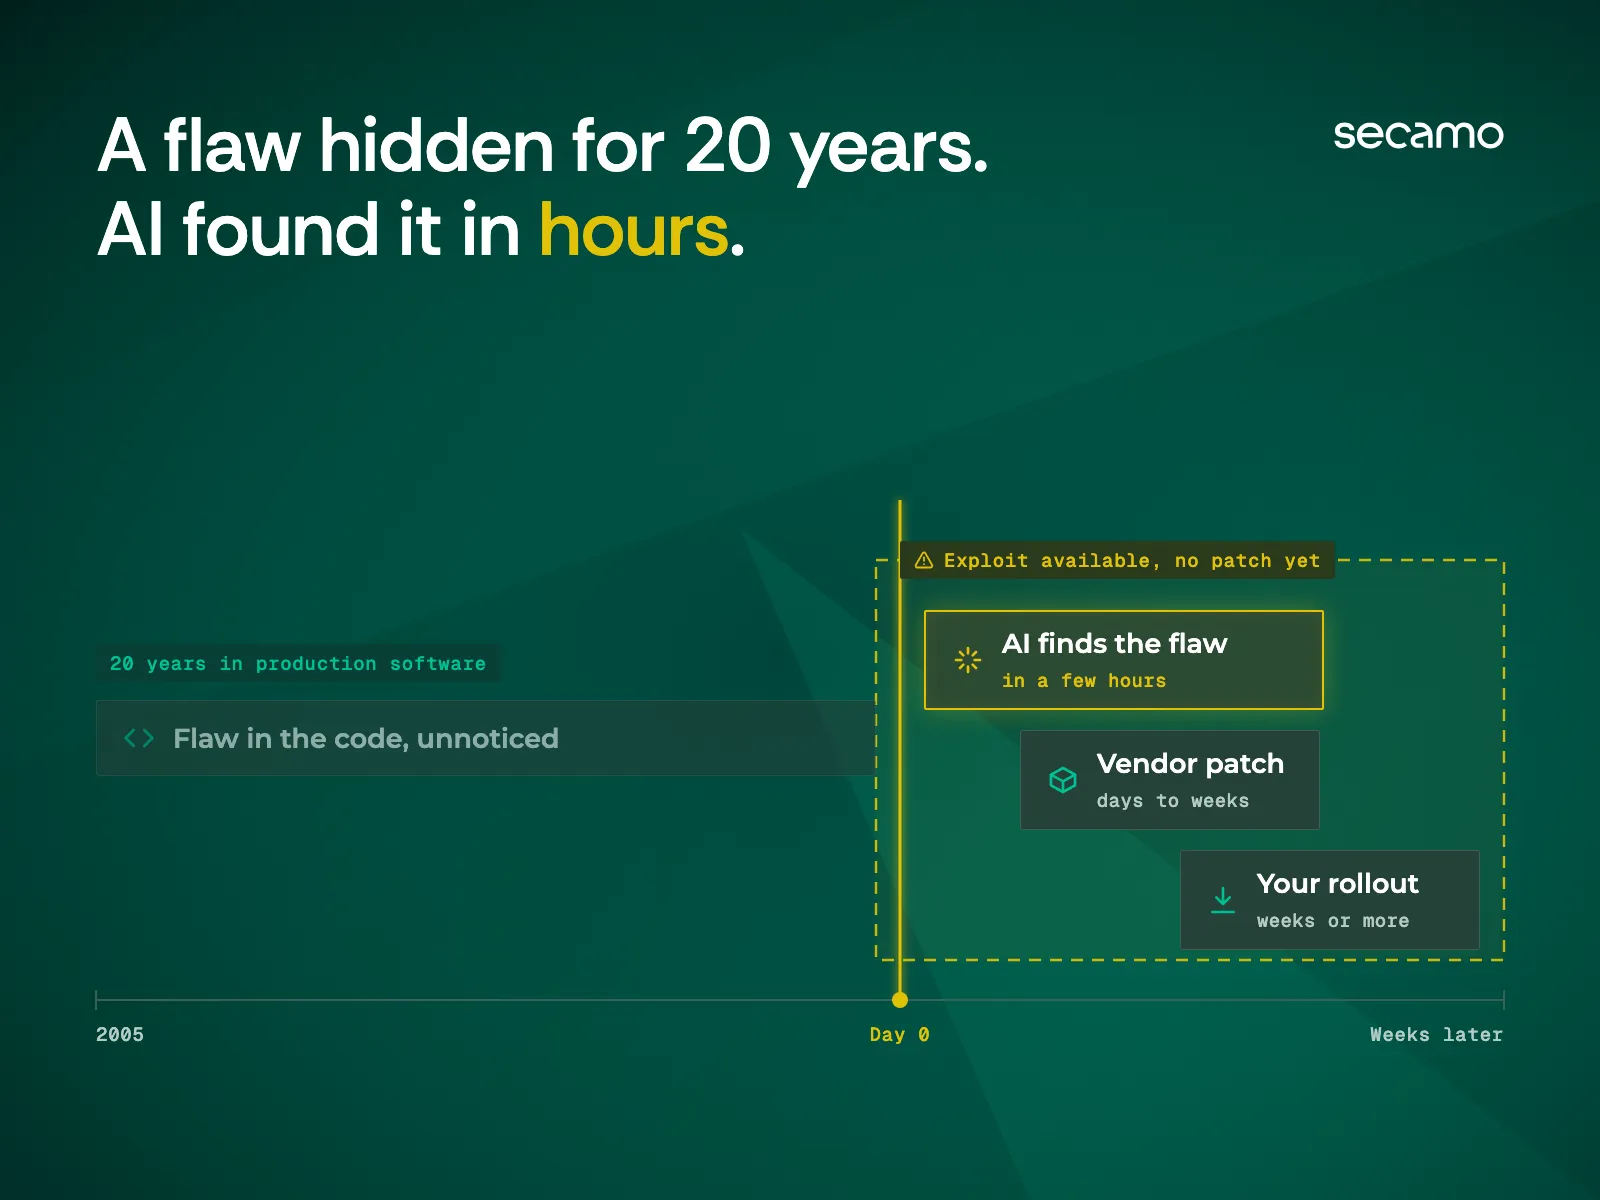
Read the article- Your company is now a target for cyber weapons that only intelligence services could affordAI models now find zero-day vulnerabilities in hours that human experts missed for decades. Vendors cannot patch fast enough and companies cannot roll out fast enough. What that means for your risk register, and five things to do now.

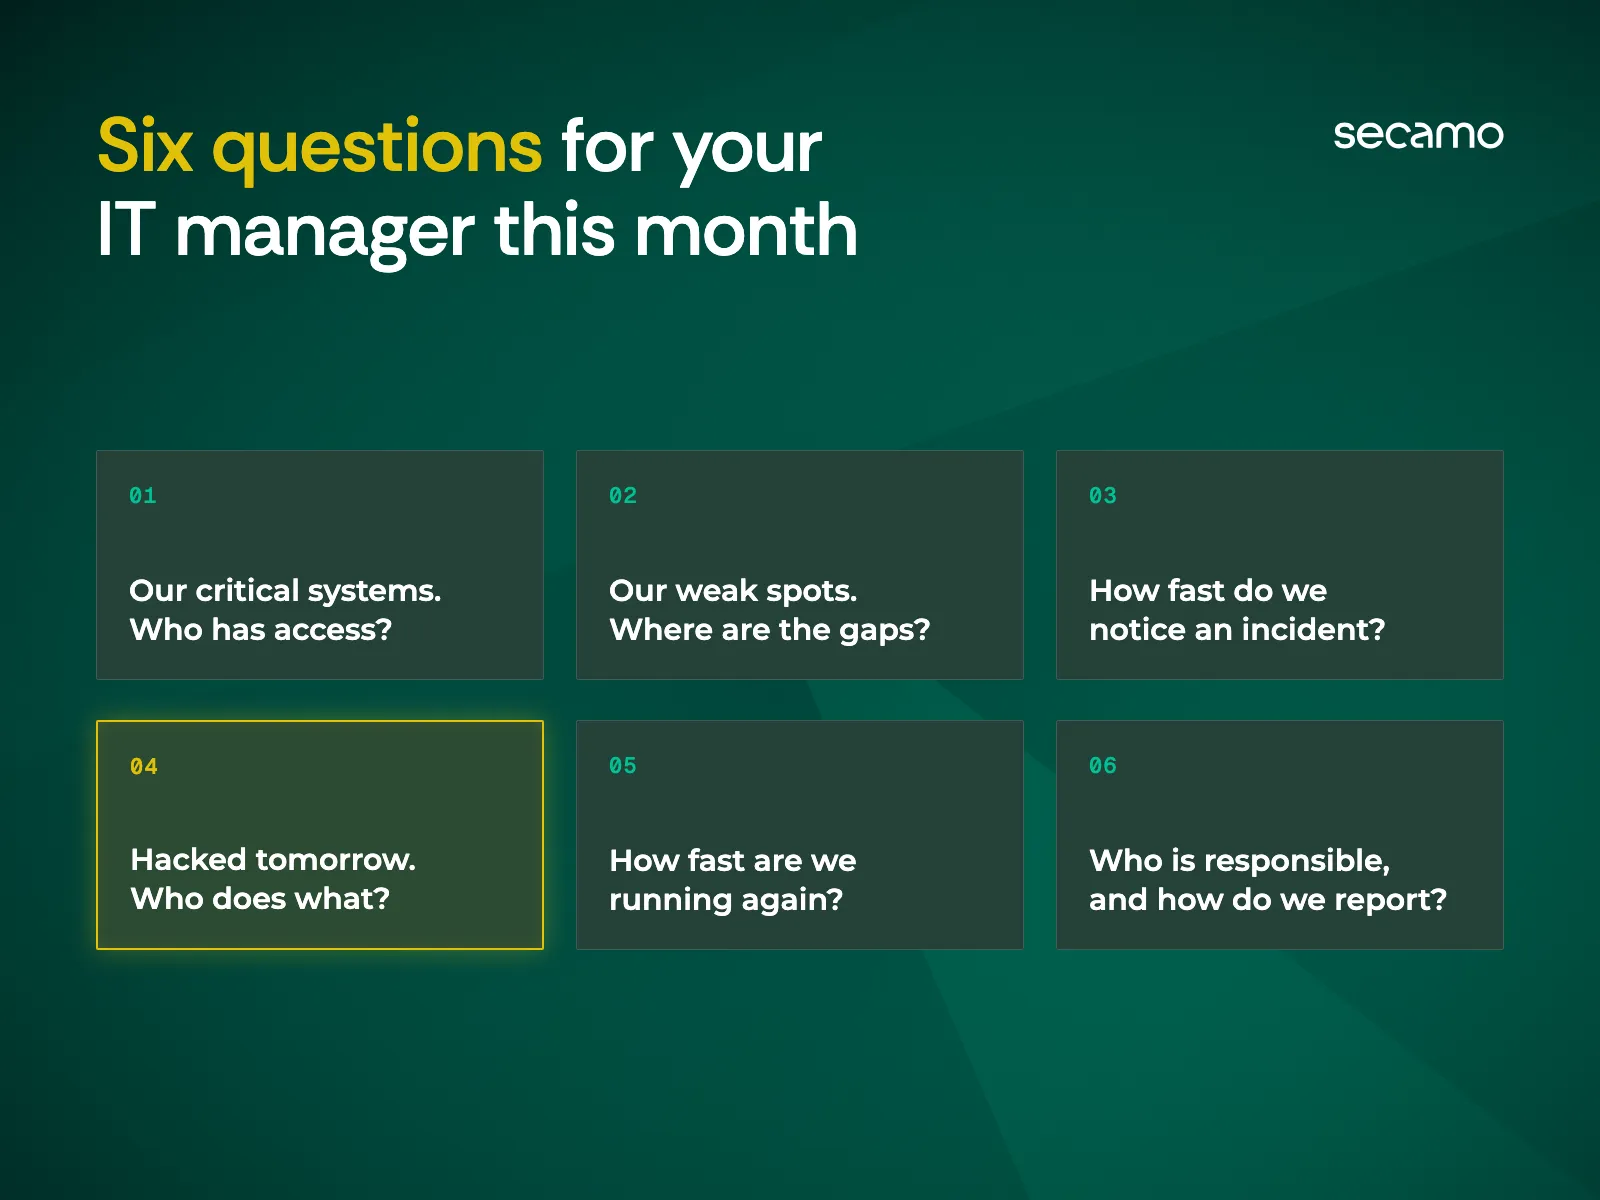
- A message for every CEO who does not always listen to their IT managerJoost Daem, founder of Secamo, on why your organisation’s resilience depends on you, and the six questions to discuss with your IT manager this month.
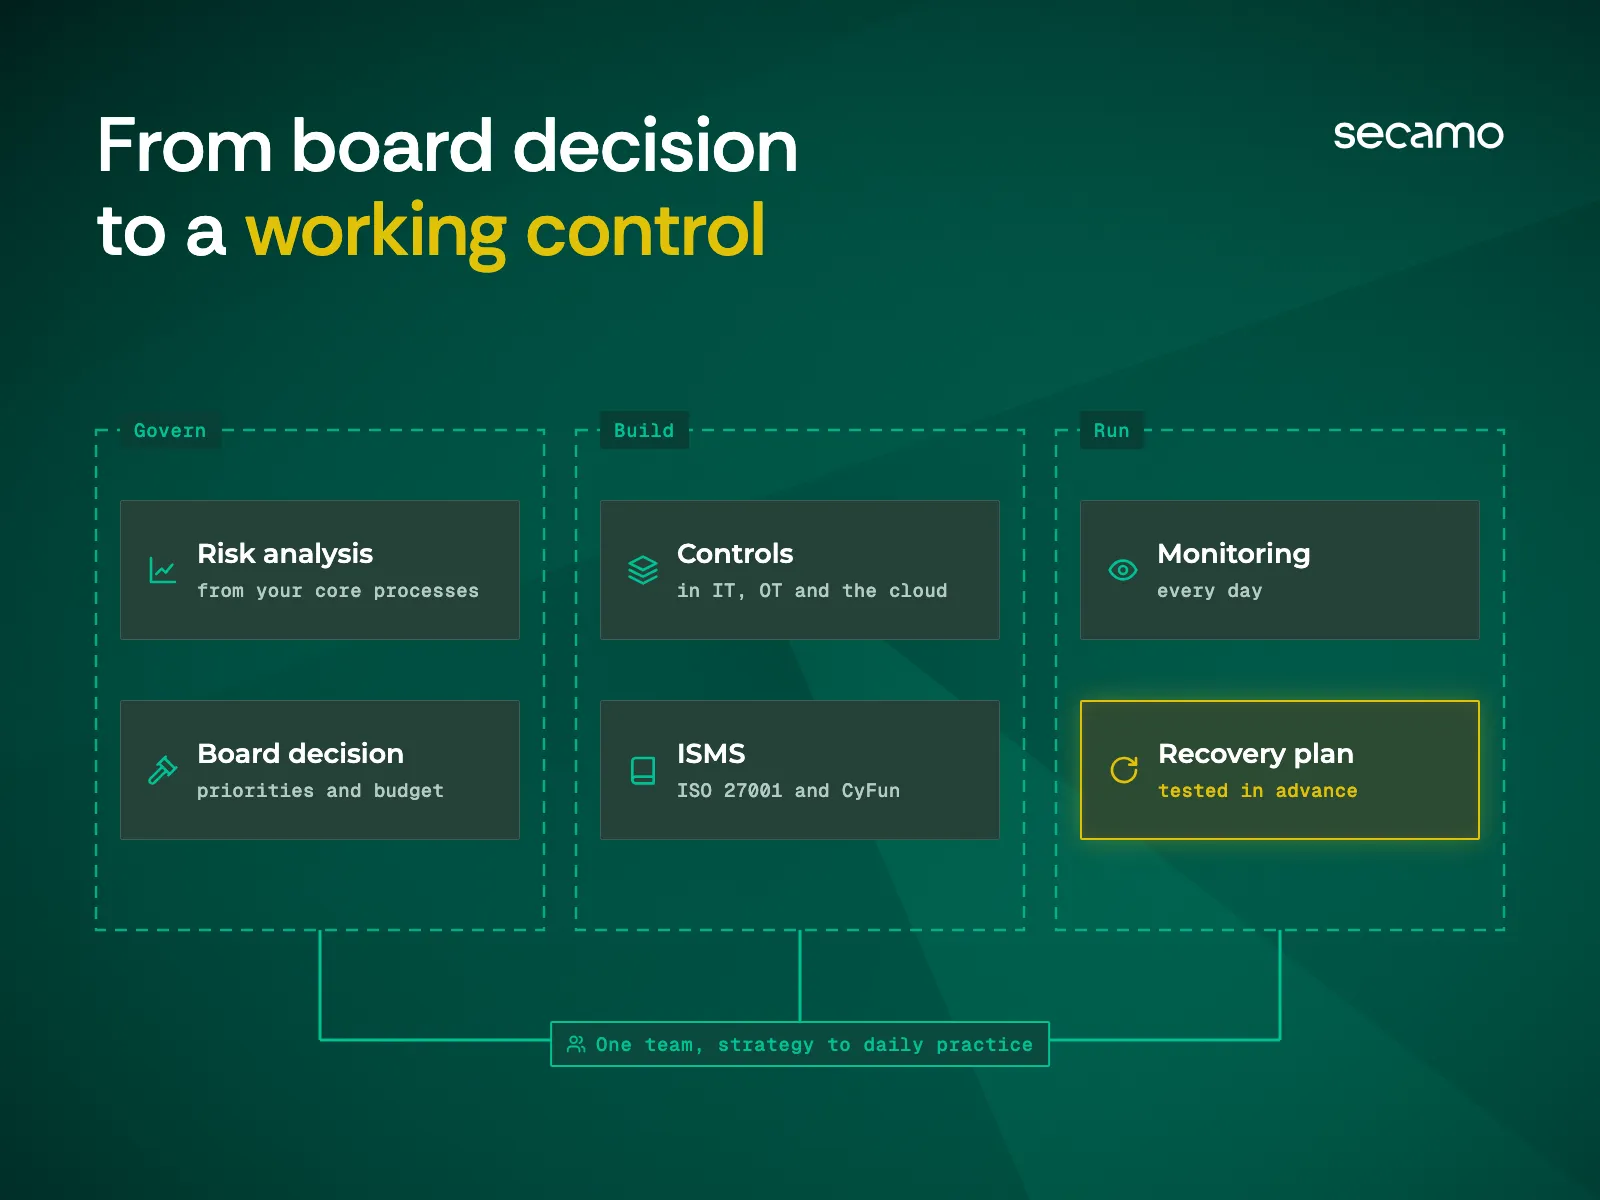
- What sets Secamo apart: cyber strategy and practice in one teamSecamo connects cyber strategy to daily operations: risk analysis that leads to board decisions, controls that work in IT, OT and the cloud, and recovery plans that are tested before they are needed.
- E-Solutions rebrands as Secamo: secure for the long runE-Solutions becomes Secamo. Same leadership, same team and the same cybersecurity strategy and execution services, under a new name and identity.
Next step
What do you want to build next?
Bring the AI pilot, the audit date or the project that is waiting on security. In a first call we work out what it takes to move it forward.
- 01Tell us what you are planning. A few lines are enough.
- 02We call you back to talk it through.
- 03You get a first view of where to start and what it takes.
Plan a first call
No preparation needed. Bring what you have.