Getting things done
What sets Secamo apart: cyber strategy and practice in one team
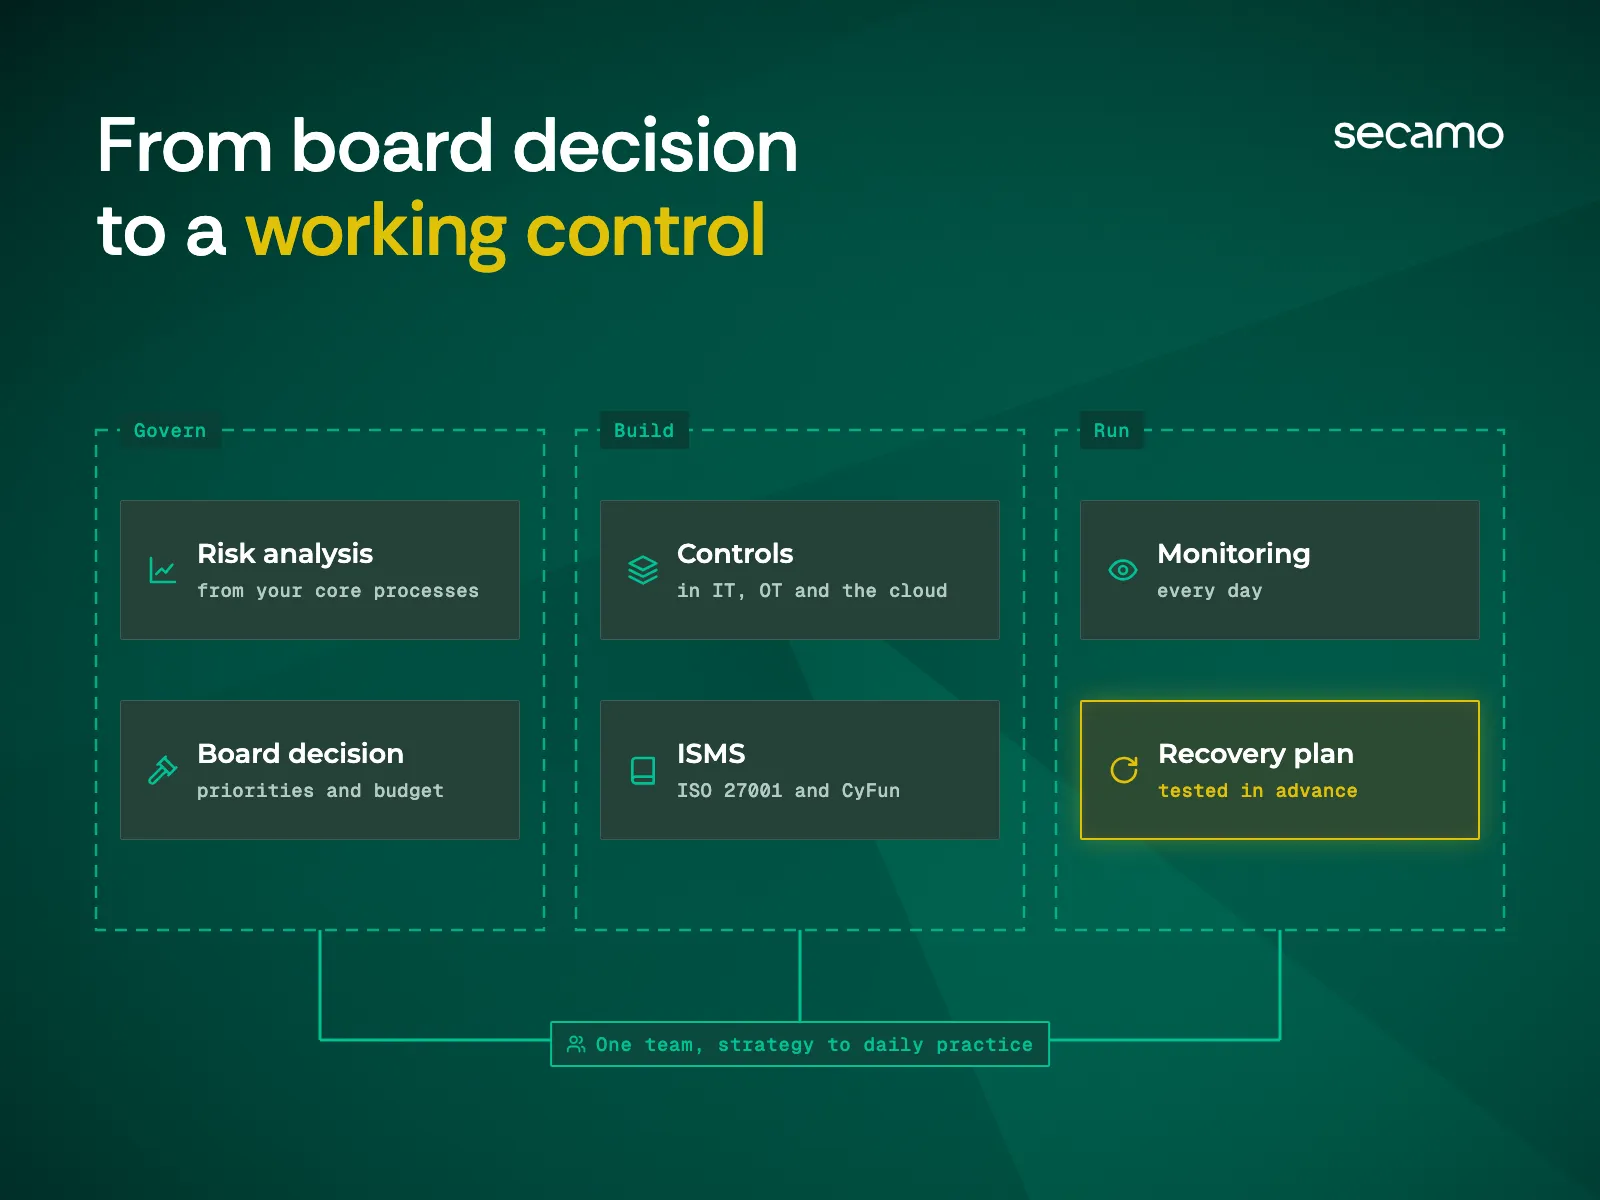
Secamo connects cyber strategy to daily operations: risk analysis that leads to board decisions, controls that work in IT, OT and the cloud, and recovery plans that are tested before they are needed.

Secamo, founded by Joost Daem, has more than 25 years of experience helping organisations strengthen their digital resilience for the long term. The firm supports clients from strategic risk analysis through to operational delivery, always from one principle: contribute to the resilience of the business. Technology and compliance follow from that.
For Secamo, cybersecurity is an integral part of enterprise risk management. When cyber risk sits inside the wider risk framework, investments become logical, proportionate and strategically grounded. That is how Secamo acts as your strategic guide in resilience and risk management.
“Start from your critical business processes to plan your resilience. When you focus on resilience, compliance comes along as a side effect.”
Strategy
Secamo translates complex cyber domains into clear management decisions. It starts with drawing up or strengthening a cybersecurity strategy, including governance and a mature information security management system (ISMS). Well-known frameworks such as ISO 27001 and the Belgian Cyber Fundamentals framework (CyFun) are integrated along the way.
By starting from the core processes and how they create value, Secamo helps organisations set the right priorities in a crisis. That prevents lost time, wrong decisions and reputational or financial damage.
“One day something will go wrong. Then you need plans that have been tested and that work,” says Joost Daem. “Does the CEO trust that the plans on paper will actually work? Because every organisation faces a cyber incident sooner or later.”
Next to strategic guidance, Secamo supports organisations operationally. The firm follows up alerts of possible incidents, analyses them and coordinates the response where needed. At the same time, Secamo optimises IT, OT and cloud processes, simplifies and automates them where possible, and so creates a safer working environment for employees.
“We stand next to our clients during a cyber incident. And we make sure their processes and cyber controls are built so that the damage stays limited.”
Resilience
For Secamo, cybersecurity is about resilience as much as prevention. Detect, respond and recover are the key words. Secamo helps companies think through the scenarios nobody wants to face. What happens if IT goes down completely? Which processes have to restart first? How do we keep functioning, even if we are forced to work on paper?
“Which processes do you restart first after an incident? That only becomes clear when you think from business processes and value creation,” says Joost Daem.
What sets Secamo apart is the combination of strategy and practice. The firm first takes an honest, thorough look at what an organisation already does, and adds to it where needed. Then it implements measures that work in practice, in IT, OT and the cloud. Finally, it tests and improves continuously, so that backups and recovery procedures hold when things go wrong.
Partnership
Secamo works as a close partner: short lines, direct expertise and long-term relationships. The firm focuses on sectors where it can add exceptional value, with industrial environments at the core.
“We work end to end, flexibly and without noise. Clients stay with us for years because we move fast, think along with them and do what is needed,” says Joost Daem.
People matter as much as technology. Secamo builds awareness and behavioural change into every engagement, from workshops to hands-on training on phishing, social engineering and safe working habits.
Secamo helps organisations understand their cyber risks, make conscious choices within their risk appetite, make processes and systems robust, handle incidents operationally and become compliant without unnecessary cost. The result is a sustainable, pragmatic cyber strategy that works on the shop floor and in the boardroom.
“If the house burns down, the safe, your backup, has to hold. We test that. We keep working together. We think for the long term.”